- Subject Overview: vlt 1.0 Redefines Package Management With Native Malware Defense and Graph Queries — Key developments across Infrastructure.
- Technical Context: Detailed analysis of architectural changes, product capabilities, and engineering metrics.
- Industry Impact: Key implications for software developers, startup founders, and enterprise technology adopters.
The Architectural Evolution Beyond Legacy Package Managers
The JavaScript ecosystem has long relied on legacy package managers that were architected during a vastly different era of web development. As modern codebases scale to hundreds of thousands of transitive dependencies, traditional tools like npm and yarn frequently struggle with performance bottlenecks, high disk I/O, and opaque dependency trees. Version 1.0 of vlt arrives as a ground-up reimagining of how packages are resolved, fetched, and deployed across diverse environments, providing an immediate drop-in replacement that respects existing lockfiles while drastically accelerating developer velocity.
At the core of this new tool is a radically optimized resolution engine designed to handle massive monorepos and distributed microservice architectures with ease. By replacing outdated sequential parsing algorithms with concurrent, memory-efficient graph operations, vlt minimizes latency during routine dependency synchronization tasks. Developers transitioning their local environments and continuous integration pipelines can expect substantial reductions in installation times, freeing up valuable computational resources and eliminating frustrating build pipeline friction.
Furthermore, the drop-in nature of vlt ensures that teams do not need to rewrite their deployment scripts or alter their CI/CD configurations to reap immediate operational rewards. The tooling maintains complete compatibility with existing registry standards and authorization protocols, allowing organizations to adopt next-generation performance enhancements without undergoing risky, disruptive migrations. This seamless integration philosophy is critical for enterprise adopters who demand absolute stability alongside cutting-edge optimization.
Advanced Phased Installs and Granular Graph Querying
One of the standout innovations within the vlt 1.0 release is the introduction of phased installations. Traditional package managers execute synchronous fetch-and-extract routines that can lock up build agents and degrade developer experience during large-scale updates. vlt decouples these phases, allowing systems to prioritize critical runtime dependencies while deferring non-essential assets, thereby optimizing resource allocation and dramatically reducing time-to-first-build in complex cloud environments.
Complementing phased installations is a powerful dependency graph query capability that exposes unprecedented visibility into project architectures. Instead of forcing developers to parse chaotic text-based tree outputs, vlt provides a querying interface that enables teams to inspect specific transitive dependencies, audit license compliance, and analyze package weight programmatically. This level of granular insight transforms the package manager from a simple file downloader into an active diagnostic tool for software composition analysis.
Engineering teams can leverage these graph queries within automated governance frameworks to enforce strict internal policies regarding code reuse and architectural boundaries. By querying the dependency graph directly from the command line or integrated development environments, architects can instantly detect circular references, bloated modules, and unauthorized package versions before they ever reach production environments, fundamentally raising the baseline quality of enterprise software deliverables.
Proactive Malware Blocking and Supply Chain Defense
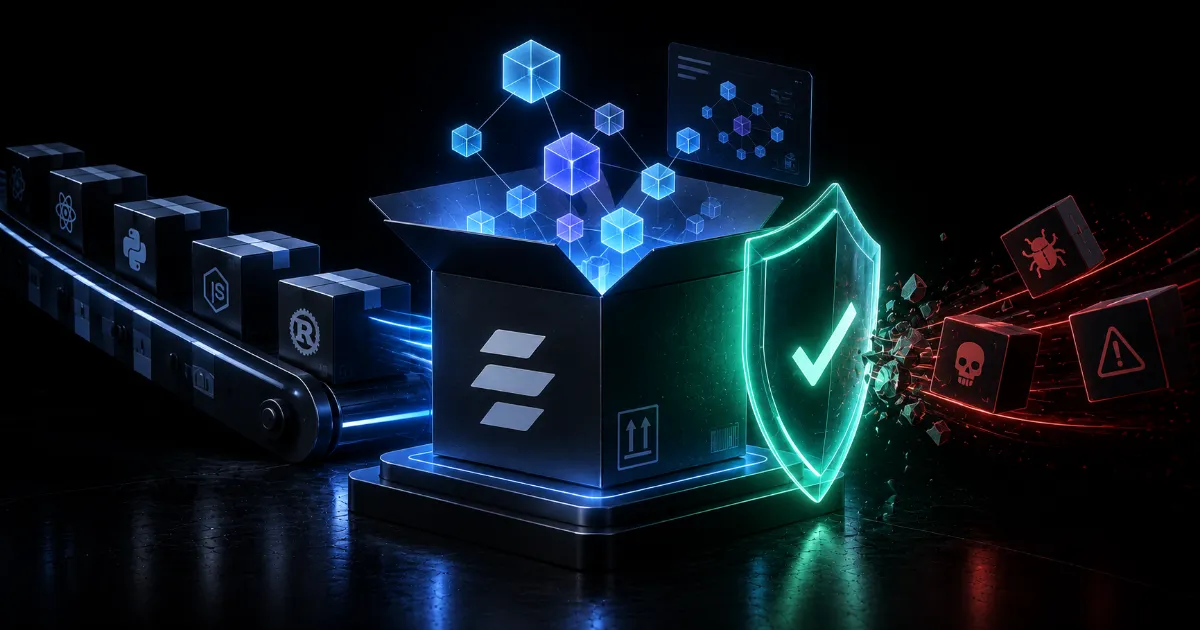
Software supply chain security has emerged as one of the most critical threat vectors facing modern software organizations. Malicious actors frequently target public registries by publishing typosquatted packages or injecting malicious payloads into legitimate, unmaintained libraries. vlt addresses this existential threat head-on by embedding proactive malware-blocking mechanisms directly into the core resolution and installation pipeline, shifting security left to the moment a dependency is first requested.
Unlike reactive scanners that rely solely on periodic database updates, vlt employs heuristic analysis and behavioral pattern matching to identify suspicious installation scripts and unauthorized network calls during package execution. By intercepting these hazardous behaviors before the code can execute arbitrary commands on developer machines or CI/CD runners, the tool creates an effective quarantine barrier against zero-day supply chain attacks and sophisticated social engineering campaigns targeting open-source maintainers.
This security-first architecture empowers organizations to enforce zero-trust principles across their entire software development lifecycle without encumbering everyday developer workflows. As regulatory compliance frameworks demand rigorous provenance tracking and artifact verification, having an intelligent package manager capable of intercepting malicious payloads at the ingestion layer provides a vital layer of defense for modern engineering organizations.
Strategic Outlook for the JavaScript Ecosystem
The arrival of vlt 1.0 marks a significant inflection point in the maturation of JavaScript tooling, signaling that the community is ready to move beyond legacy paradigms. By addressing longstanding performance pain points while baking enterprise-grade security and graph analytics directly into the foundational layer, the project sets a new benchmark for what developers should expect from their dependency management infrastructure in the coming decade.
For enterprise technology leaders, adopting vlt represents an opportunity to fortify software supply chains while simultaneously boosting developer productivity through faster, more reliable build cycles. As the ecosystem continues to embrace these advanced architectural patterns, the tooling landscape will undoubtedly shift toward smarter, more observable infrastructure components that prioritize safety and speed above all else, ensuring JavaScript remains robustly equipped for the most demanding enterprise workloads.
Related Coverage on TechRoro
- [Infrastructure] Unlocking High-Performance Generative Workloads With GLM-5.3 and DigitalOcean Partnership
- [Infrastructure] Modernizing Mainframe Access Control With Identity Based Boundary Architecture
- [Infrastructure] AWS Unveils Serverless Hybrid Cloud Orchestration Pattern with Amazon EKS Anywhere