- Subject Overview: The Identity Verification Crisis Exposing Millions Of Compromised Driver Licenses — Key developments across Gadgets.
- Technical Context: Detailed analysis of architectural changes, product capabilities, and engineering metrics.
- Industry Impact: Key implications for software developers, startup founders, and enterprise technology adopters.
The Architecture Of Digital Identity Honey Pots
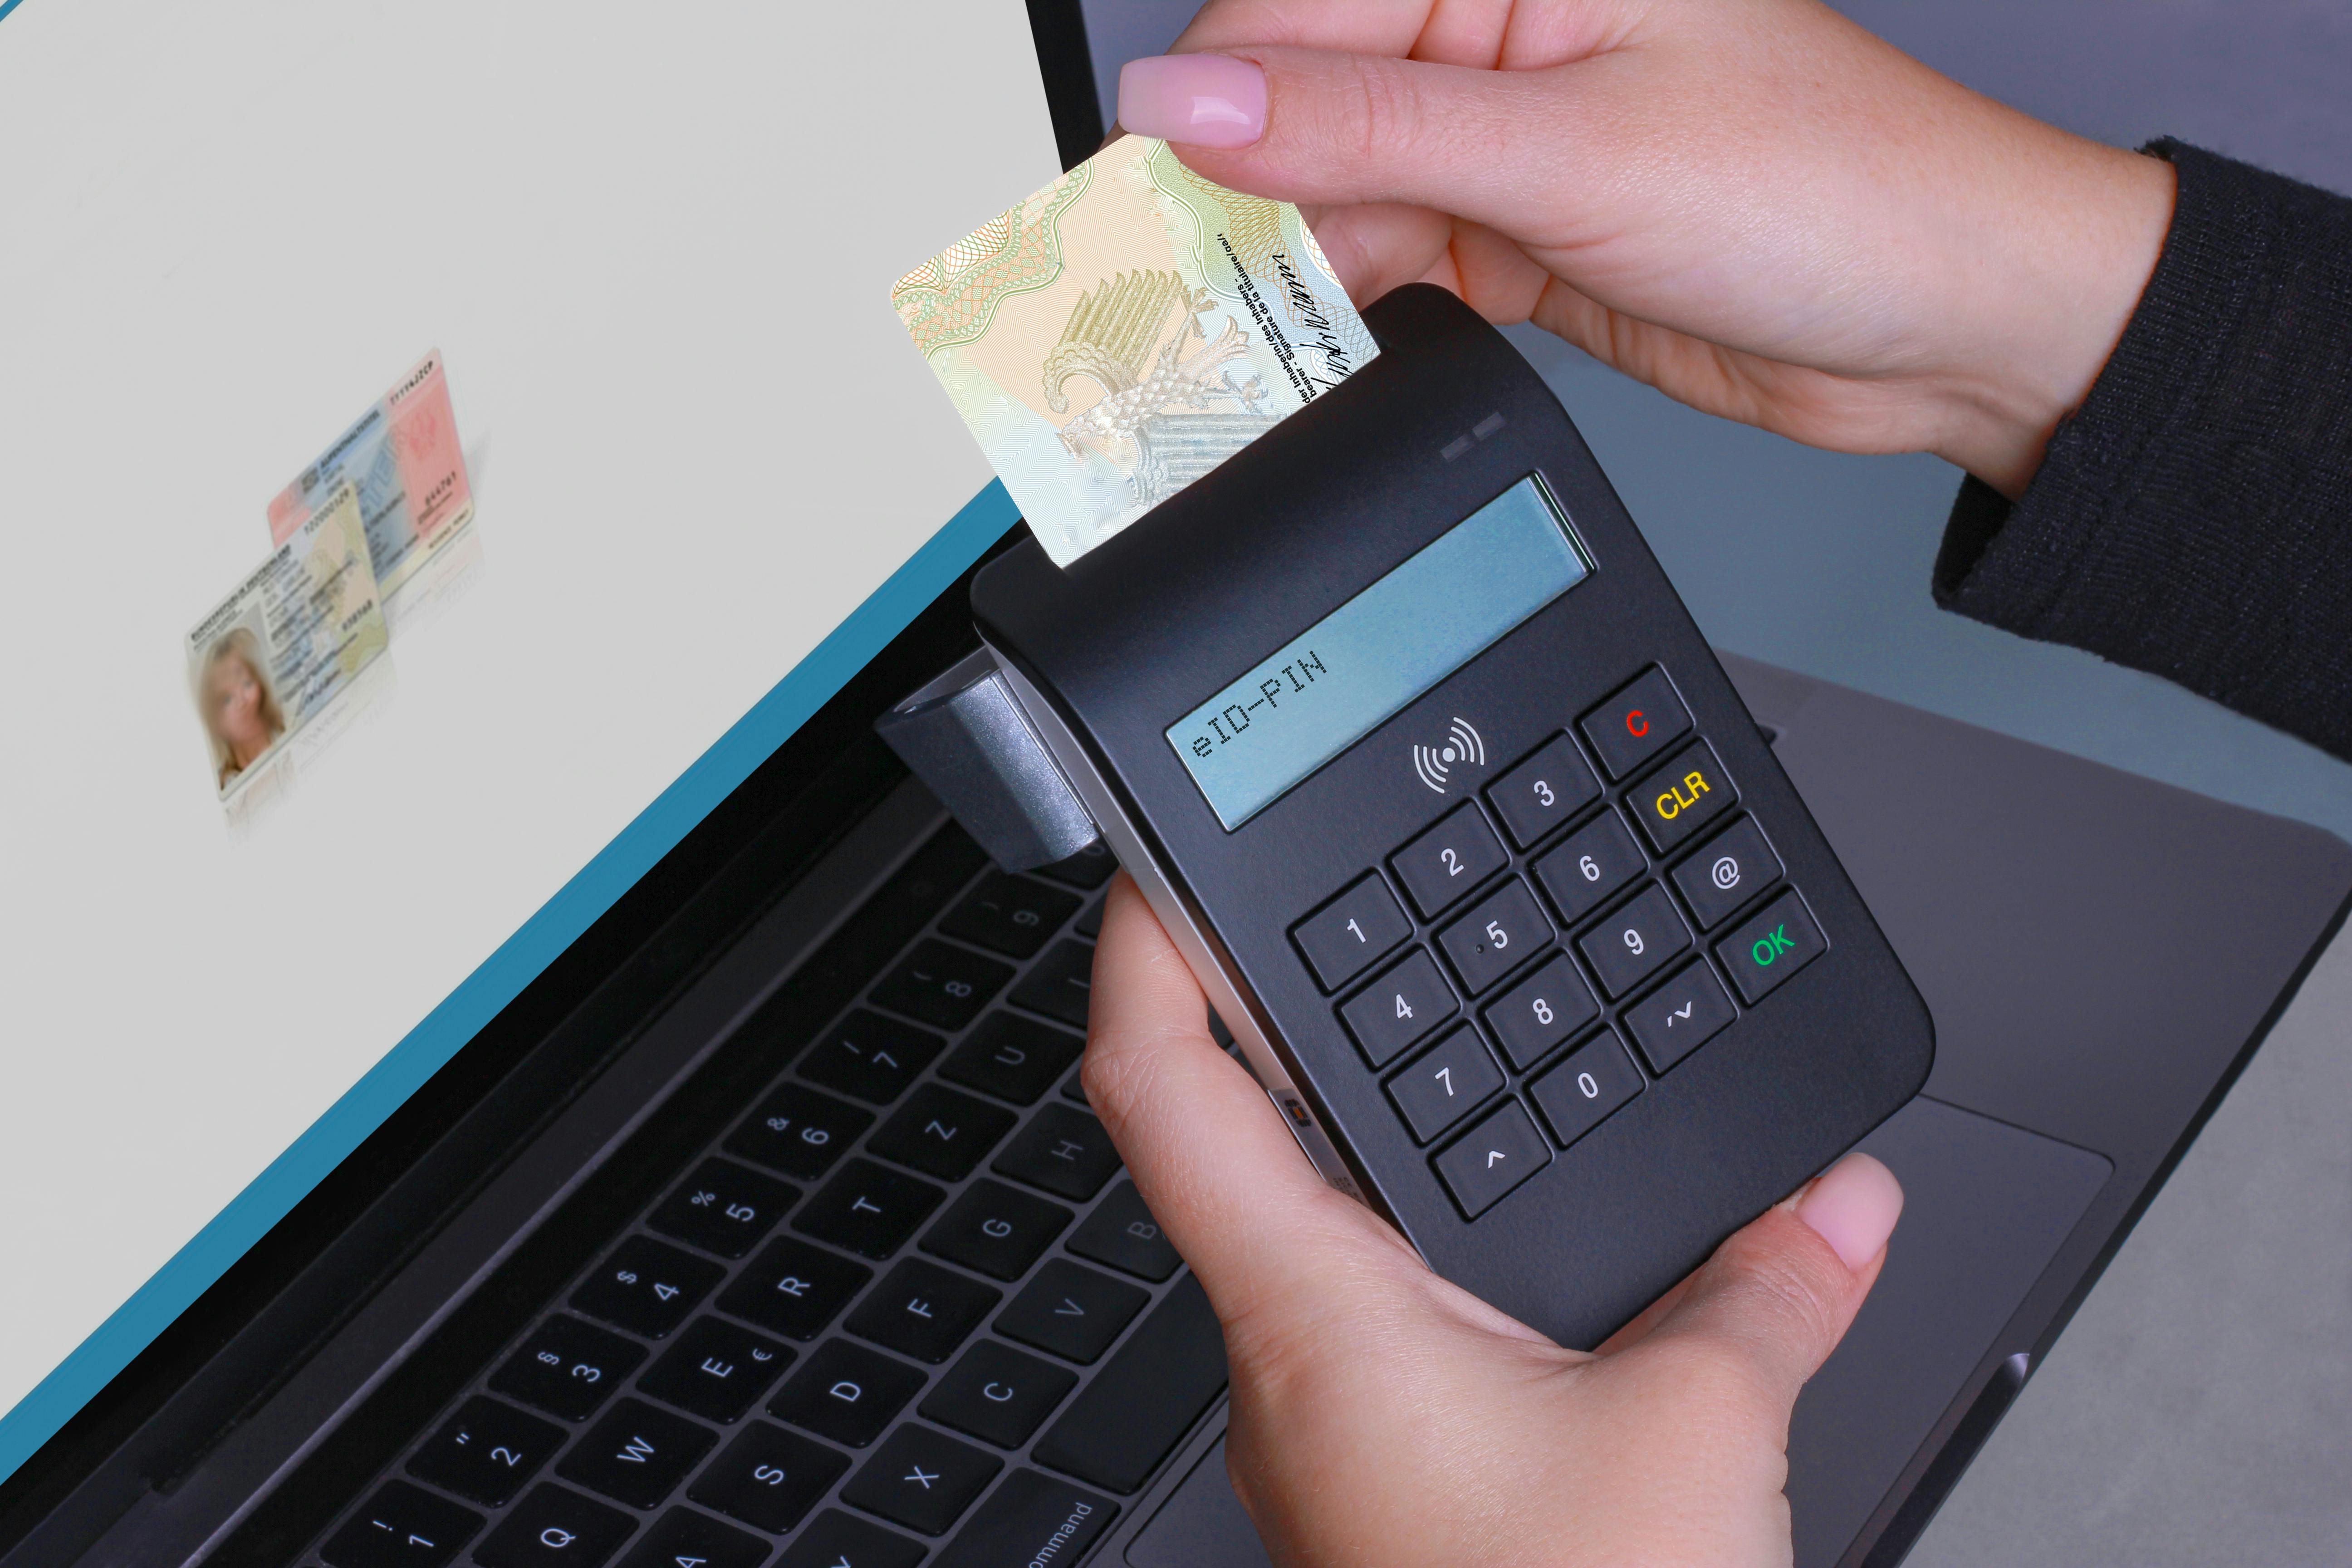
In the modern digital economy, identity verification has become a mandatory frictionless hurdle for accessing financial services, telecommunications, and online platforms. To comply with stringent regulatory frameworks and prevent fraud, corporations routinely collect, process, and store millions of high-resolution identity documents, including driver's licenses, passports, and biometric scans. However, this centralized accumulation of hyper-sensitive personal data creates lucrative honey pots that attract sophisticated cybercriminal syndicates seeking massive data monetization opportunities.
The core architectural flaw in current identity verification models lies in the permanent storage of raw, unmasked identification documents across third-party vendor servers. When enterprises outsource their know-your-customer processes to specialized verification providers, data is frequently retained far beyond its operational necessity to train machine learning models or facilitate recurring audits. This accumulation of permanent records transforms routine identity verification platforms into high-value targets where a single security perimeter failure exposes millions of citizens to lifelong identity theft risks.
Furthermore, the lack of standardized cryptographic safeguards across the identity verification sector leaves vast troves of personal identifiable information vulnerable to simple database misconfigurations and credential stuffing attacks. Unlike credit card numbers, which can be canceled and reissued following a breach, foundational identity documents like driver's licenses remain static identifiers throughout a person's life. Consequently, when millions of these records appear on illicit data marketplaces, the resulting security fallout affects victims across every digital service relying on traditional document-based authentication.
Systemic Failures In Vendor Risk Management
The recent exposure of 153 million driver's license records starkly illustrates the systemic vulnerabilities inherent in third-party vendor ecosystems and corporate data governance policies. Enterprises frequently delegate critical security responsibilities to external verification providers without maintaining continuous oversight or enforcing stringent data minimization protocols. This outsourcing creates obscured operational blind spots where internal vulnerabilities remain unpatched until a catastrophic data exfiltration event makes national headlines.
Regulatory compliance frameworks, while well-intentioned, often fail to enforce real-time technical defenses, relying instead on retroactive punitive measures after breaches occur. Organizations focus heavily on checkbox compliance rather than implementing zero-trust architectures that encrypt identity documents at rest, in transit, and during active processing states. As long as centralized service providers continue to hoard unencrypted identity scans in massive relational databases, malicious actors will find immense financial incentive to breach these repositories.
The commodification of stolen identity documents on dark web forums demonstrates the sophisticated automation driving modern cybercrime economies. Threat actors utilize specialized scraping frameworks and automated validation tools to verify the authenticity of leaked driver's licenses before packaging them for bulk resale to financial fraudsters. This industrialization of identity theft renders traditional consumer-level credit monitoring services largely ineffective against targeted synthetic identity creation and account takeover attacks.
The Technical Imperative For Decentralized Verification
Mitigating the escalating crisis of digital identity theft requires a fundamental paradigm shift away from centralized honey pots toward privacy-preserving, decentralized verification technologies. Modern cryptographic primitives, such as zero-knowledge proofs and decentralized identifiers, offer a viable path forward by enabling users to prove their eligibility, age, or identity attributes without exposing raw document scans to third-party servers. In a zero-knowledge architecture, the verifying entity receives only a cryptographically signed boolean confirmation rather than a permanent copy of a driver's license.
Implementing decentralized identity systems eliminates the incentive for cybercriminals to target central databases, as there is no consolidated repository of raw personal documents left to plunder. Developers and security architects must champion protocols that grant users absolute ownership and control over their identity credentials, storing sensitive information locally on secure hardware devices rather than cloud-based enterprise silos. This architectural transformation aligns regulatory compliance with robust privacy engineering principles, protecting both businesses and consumers.
In addition to cryptographic innovation, organizations must immediately adopt strict data lifecycle management policies that mandate the automated deletion of raw identity scans immediately following verification. By transitioning to stateless verification pipelines that process document attributes in volatile memory without persisting files to disk, companies drastically reduce their risk profile. Such technical measures ensure that even if an edge server is compromised, no long-term archives of sensitive citizen data are available for extraction.
Strategic Outlook For Digital Trust Infrastructure
The exposure of 153 million driver's licenses serves as an undeniable wake-up call for the global technology sector regarding the unsustainable nature of current identity verification practices. As digital interactions continue to expand across global markets, rebuilding public trust in online authentication systems is paramount for economic stability and democratic security. Governments, standards bodies, and private enterprises must collaborate to mandate advanced cryptographic standards that eliminate the collection of honeypot data.
Ultimately, the future of secure identity verification relies on moving beyond static, easily forged documents toward dynamic, cryptographic credentials that prioritize user privacy and data minimization. Industry leaders who proactively adopt decentralized and zero-knowledge verification frameworks will successfully insulate themselves from catastrophic data breaches while empowering users with true digital sovereignty. The era of storing millions of vulnerable identity documents must end to secure the digital frontier against persistent malicious threats.
Related Coverage on TechRoro
- [Gadgets] Understanding Display Degradation Mitigating Burn-In Risks Across Modern Television Technologies
- [Gadgets] Tim Cook Leaves Behind an Environmental Legacy Threatened by AI Infrastructure Demands
- [Gadgets] Blue Origin Secures Prestigious NASA Contract to Build Next Generation Mars Telecommunications Orbiter